Academic simulation
Guilty Sector
Digital forensics course project
A course-based case exercise that examined memory and disk artifacts, recovered a test password, and extracted hidden data. The work was conducted as a simulation, not a real incident investigation.
Selected project images are shown below.
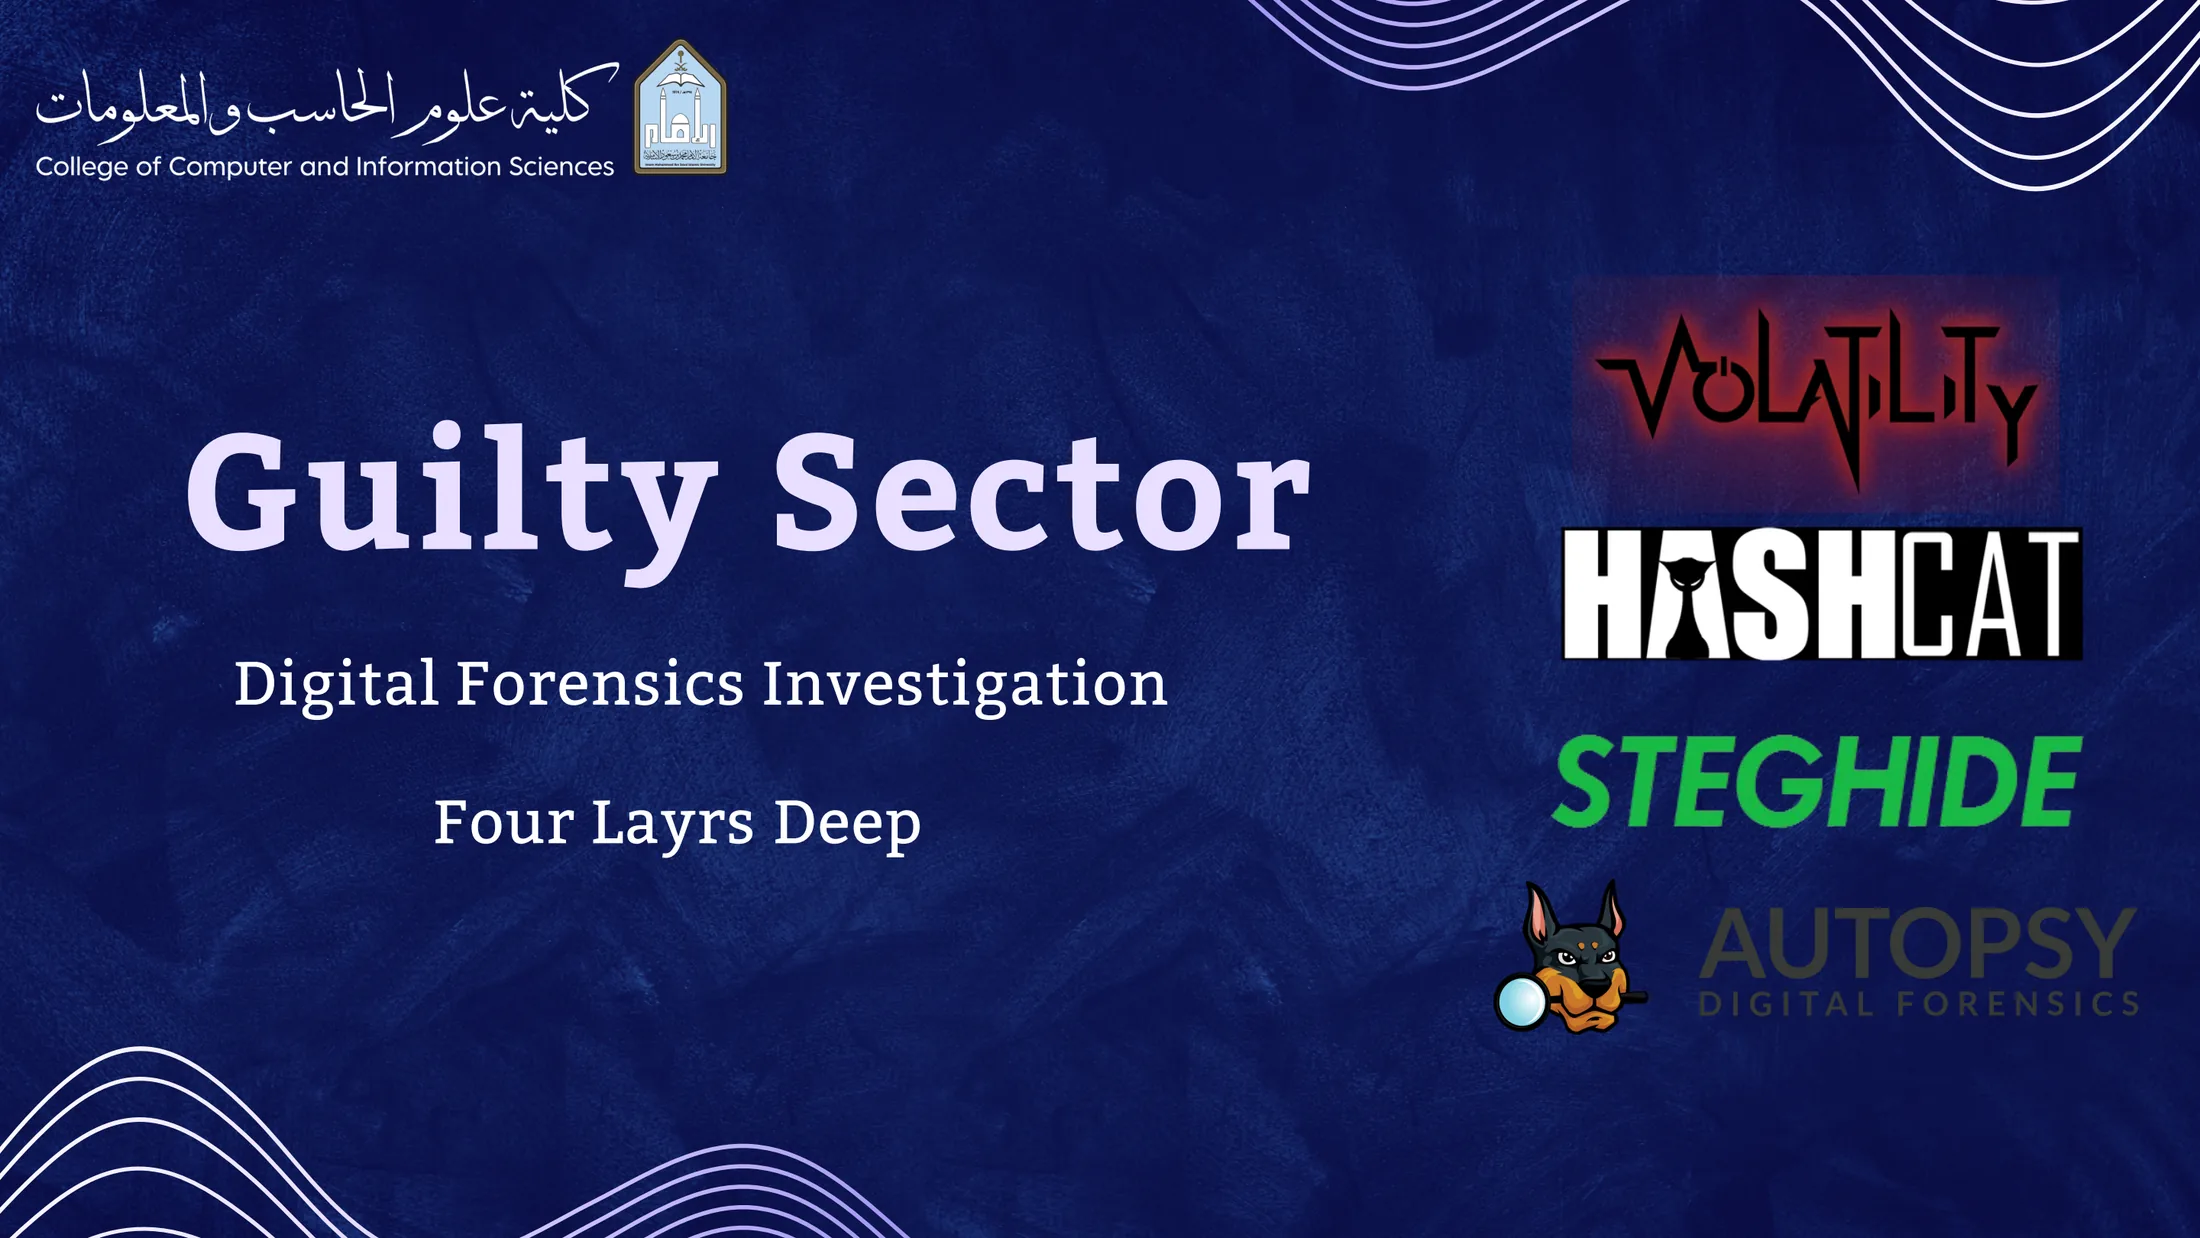
Scope & approach
- Memory and process artifact analysis with Volatility
- Disk artifact review and deleted-file recovery with Autopsy
- Test password hash recovery with Hashcat
- Steganography analysis with Steghide